Every app in your order flow can leak your customers' information.
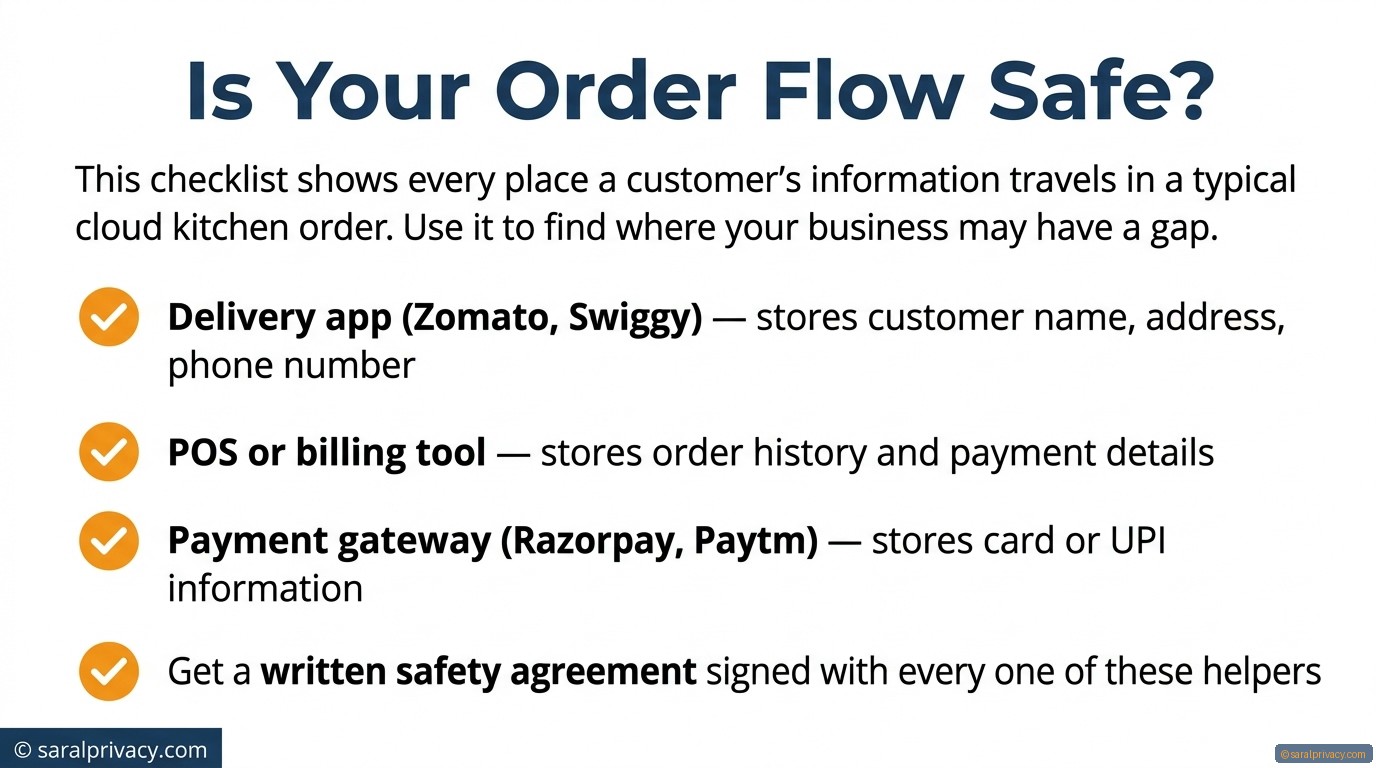
A customer orders biryani on Zomato. Their phone number, address, and payment details travel through your POS system, a delivery app, a payment gateway, and maybe a CRM tool. That is four or five outside companies touching your customer's information. Under the new privacy law, if any one of them leaks that data — you are still responsible. Does this apply to your restaurant or cloud kitchen? Yes, it does.
Say your cloud kitchen uses Swiggy for orders, a POS machine for billing, Razorpay for payments, and WhatsApp for customer support. Each of these holds your customers' phone numbers and addresses. If Razorpay or your POS vendor has a leak, your customers are hurt. The law says you must have a written agreement with each of these helpers. You must tell them to keep data safe. You must also know how to report a leak quickly. More apps means more risk.
List every app or tool that touches your customers' phone numbers or addresses.
Ask each app vendor if they have a written data safety agreement ready to sign.
Check if your business is ready. Takes 3 minutes. Visit saralprivacy.com/assessment
“The more platforms in the order flow the more privacy discipline you need.”
Free — takes 3 minutes
Answer a few simple questions. Get your free Readiness Score — sent to your email or WhatsApp.
Check My Readiness →Take our free 3–5 minute industry assessment to find out your compliance risk level.
Take Free Assessment →मुफ़्त डाउनलोड
संपूर्ण DPDPA अनुपालन गाइड
आसान भाषा में। DPDP Rules 2025 समझने के लिए आपके व्यवसाय को जो कुछ चाहिए — फ़ाउंडर्स के लिए लिखा गया, वकीलों के लिए नहीं। अब 7 भारतीय भाषाओं में।
गाइड डाउनलोड करें →5 तैयार टेम्पलेट
सिर्फ़ पढ़िए नहीं — अनुपालन शुरू कीजिए
प्राइवेसी नोटिस, सहमति की भाषा, डेटा इन्वेंटरी, DSR SOP, वेंडर रजिस्टर। आपके ईमेल पर, मुफ़्त।
2-min reads, plain English, every morning. Free forever.
